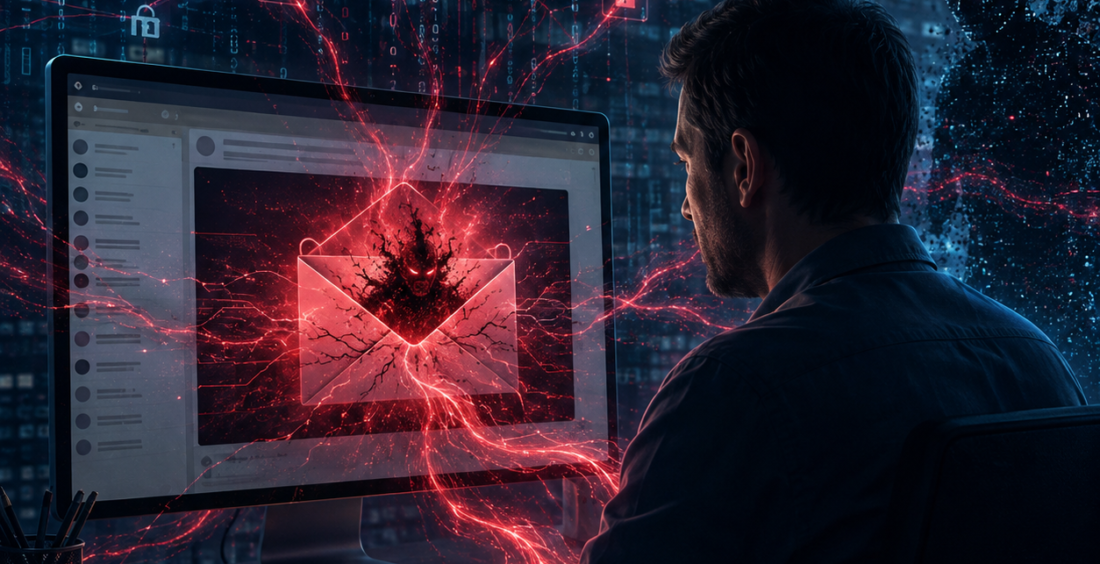
Most phishing advice assumes the victim has to do something risky. Click a link. Open an attachment. Enter a password. Half-click email attacks challenge that assumption. In these attacks, simply viewing a malicious message inside a vulnerable webmail application can trigger code that gives the attacker access to the user’s authenticated session. The victim may never download a file or type credentials into
UEFI security is easy to overlook because most people rarely think about what happens before Windows or Linux starts. UEFI firmware helps initialize hardware and launch the operating system. Secure Boot is designed to make that startup process safer by allowing trusted software to run during boot. The concern is what happens when attackers find a way into that
Code signing is meant to answer a simple question: did this software really come from the organization it claims to come from? Developers use digital certificates to sign applications, updates and other software. Operating systems and security tools can then use that signature as a trust signal. But attackers value the same trust. If criminals steal signing material or find a way to